


2024 Valid AZ-104 FREE EXAM DUMPS QUESTIONS & ANSWERS
Free AZ-104 Exam Braindumps Microsoft Pratice Exam
NEW QUESTION # 25
You plan to deploy 20 Azure virtual machines by using an Azure Resource Manager template. The virtual machines will run the latest version of Windows Server 2016 Datacenter by using an Azure Marketplace image.
You need to complete the storageProfile section of the template.
How should you complete the storageProfile section? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
...
Reference:
https://docs.microsoft.com/en-us/rest/api/compute/virtualmachines/createorupdate
NEW QUESTION # 26
You have an Azure Subscription named Subcription1.has
Subcription1 contains the virtual machines in the following table.
Subcription1 contains the virtual machines in the following table.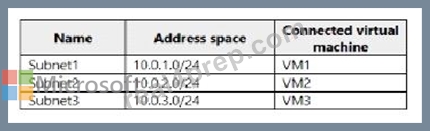
VM3 has multiple network, including a network adapter named NIC3, IP forwarding is enabled on NIC3. Routing is enabled on VM3.
You create a route table named RT1 that contains the routes in the following table.
You apply RT1 to subnet1 and Sybnet2.
For each of the following statements, select Yes if the statements is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
IP forwarding enables the virtual machine a network interface is attached to:
Receive network traffic not destined for one of the IP addresses assigned to any of the IP configurations assigned to the network interface.
Send network traffic with a different source IP address than the one assigned to one of a network interface's IP configurations.
The setting must be enabled for every network interface that is attached to the virtual machine that receives traffic that the virtual machine needs to forward. A virtual machine can forward traffic whether it has multiple network interfaces or a single network interface attached to it.
Box 1: Yes
The routing table allows connections from VM3 to VM1 and VM2. And as IP forwarding is enabled on VM3, VM3 can connect to VM1.
Box 2: No
VM3, which has IP forwarding, must be turned on, in order for VM2 to connect to VM1.
Box 3: Yes
The routing table allows connections from VM1 and VM2 to VM3. IP forwarding on VM3 allows VM1 to connect to VM2 via VM3.
References:
https://docs.microsoft.com/en-us/azure/virtual-network/virtual-networks-udr-overview
https://www.quora.com/What-is-IP-forwarding
NEW QUESTION # 27
You purchase a new Azure subscription named Subscription1.
You create a virtual machine named VM1 in Subscription1. VM1 is not protected by Azure Backup.
You need to protect VM1 by using Azure Backup. Backups must be created at 01:00 and stored for 30 days.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: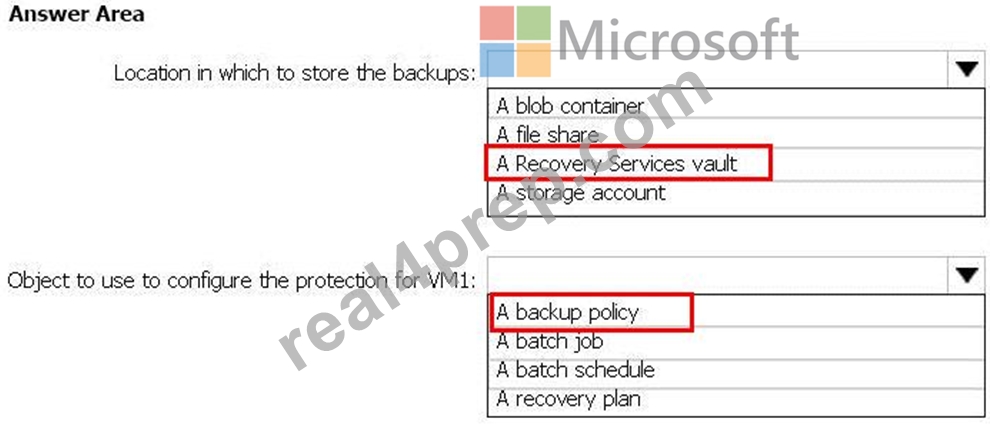
Reference:
https://docs.microsoft.com/en-us/azure/backup/backup-configure-vault
https://docs.microsoft.com/en-us/azure/backup/backup-azure-backup-faq
https://docs.microsoft.com/en-us/azure/backup/backup-azure-recovery-services-vault-overview https://docs.microsoft.com/en-us/azure/backup/backup-azure-vms-first-look-arm
https://docs.microsoft.com/en-us/azure/backup/backup-azure-recovery-services-vault-overview https://docs.microsoft.com/en-us/azure/backup/backup-azure-vms-first-look-arm
NEW QUESTION # 28
This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription named Subscription1 that contains the resources shown in the following table.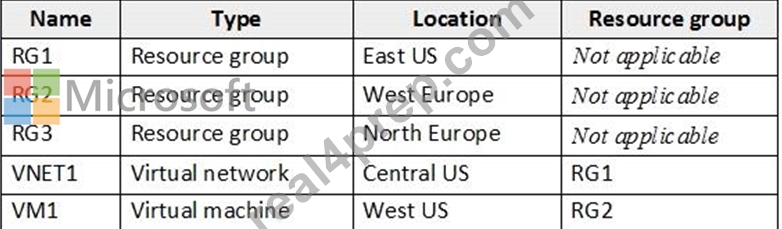
VM1 connects to a virtual network named VNET2 by using a network interface named NIC1.
You need to create a new network interface named NIC2 for VM1.
Solution: You create NIC2 in RG1 and Central US.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
The virtual machine you attach a network interface to and the virtual network you connect it to must exist in the same location, here West US, also referred to as a region.
Reference:
https://docs.microsoft.com/en-us/azure/virtual-network/virtual-network-network-interface
NEW QUESTION # 29
You have an Azure Active Directory (Azure AD) tenant named contoso.onmicrosoft.com.
The User administrator role is assigned to a user named Admin1.
An external partner has a Microsoft account that uses the [email protected] sign in.
Admin1 attempts to invite the external partner to sign in to the Azure AD tenant and receives the following error message: "Unable to invite user [email protected] - Generic authorization exception." You need to ensure that Admin1 can invite the external partner to sign in to the Azure AD tenant.
What should you do?
- A. From the Users settings blade, modify the External collaboration settings.
- B. From the Roles and administrators blade, assign the Security administrator role to Admin1.
- C. From the Custom domain names blade, add a custom domain.
- D. From the Organizational relationships blade, add an identity provider.
Answer: A
Explanation:
Reference:
https://techcommunity.microsoft.com/t5/Azure-Active-Directory/Generic-authorization-exception-inviting-Azure-AD-gests/td-p/274742
NEW QUESTION # 30
You plan to use Azure Network Watcher to perform the following tasks:
Task1: Identify a security rule that prevents a network packet from reaching an Azure virtual machine Task2: Validate outbound connectivity from an Azure virtual machine to an external host Which feature should you use for each task? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/network-watcher/network-watcher-monitoring-overview
https://docs.microsoft.com/en-us/azure/network-watcher/network-watcher-ip-flow-verify-overview
https://docs.microsoft.com/en-us/azure/network-watcher/network-watcher-connectivity-overview
NEW QUESTION # 31
You need to define a custom domain name for Azure AD to support the planned infrastructure.
Which domain name should you use?
- A. ad.humongousinsurance.com
- B. humongousinsurance.com
- C. humongousinsurance.local
- D. humongousinsurance.onmicrosoft.com
Answer: B
Explanation:
Every Azure AD directory comes with an initial domain name in the form of domainname.onmicrosoft.com.
The initial domain name cannot be changed or deleted, but you can add your corporate domain name to Azure AD as well. For example, your organization probably has other domain names used to do business and users who sign in using your corporate domain name. Adding custom domain names to Azure AD allows you to assign user names in the directory that are familiar to your users, such as '[email protected].' instead of 'alice@domain name.onmicrosoft.com'.
Scenario:
Network Infrastructure: Each office has a local data center that contains all the servers for that office. Each office has a dedicated connection to the Internet.
Humongous Insurance has a single-domain Active Directory forest named humongousinsurance.com
Planned Azure AD Infrastructure: The on-premises Active Directory domain will be synchronized to Azure AD.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/fundamentals/add-custom-domain
NEW QUESTION # 32
You have an Azure Migrate project that has the following assessment properties:
Target location: East US
Storage redundancy: Locally redundant
Comfort factor: 2.0
Performance history: 1 month
Percentile utilization: 95th
Pricing tier: Standard
Offer: Pay as you go
You discover the following two virtual machines:
A virtual machine named VM1 that runs Windows Server 2016 and has 10 CPU cores at 20 percent utilization
A virtual machine named VM2 that runs Windows Server 2012 and has four CPU cores at 50 percent utilization
How many CPU cores will Azure Migrate recommend for each virtual machine? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: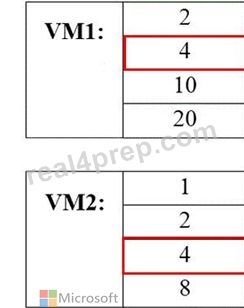
NEW QUESTION # 33
You plan to move services from your on-premises network to Azure.
You identify several virtual machines that you believe can be hosted in Azure. The virtual machines are shown in the following table.
Which two virtual machines can you access by using Azure migrate? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. Sea-DC01
- B. NYC-FS01
- C. BOS-DB01
- D. Sea-CA0l
- E. Hou-NW01
Answer: B,C
Explanation:
Azure Migrate provides a centralized hub to assess and migrate to Azure on-premises servers, infrastructure, applications, and data. It provides the following:
Unified migration platform: A single portal to start, run, and track your migration to Azure.
Range of tools: A range of tools for assessment and migration. Azure Migrate tools include Server Assessment and Azure Migrate: Server Migration. Azure Migrate also integrates with other Azure services and tools, and with independent software vendor (ISV) offerings.
Assessment and migration: In the Azure Migrate hub, you can assess and migrate:
Servers: Assess on-premises servers and migrate them to Azure virtual machines or Azure VMware Solution (AVS) (Preview).
Databases: Assess on-premises databases and migrate them to Azure SQL Database or to SQL Managed Instance.
Web applications: Assess on-premises web applications and migrate them to Azure App Service by using the Azure App Service Migration Assistant.
Virtual desktops: Assess your on-premises virtual desktop infrastructure (VDI) and migrate it to Windows Virtual Desktop in Azure.
Data: Migrate large amounts of data to Azure quickly and cost-effectively using Azure Data Box products.
Based on this information let's analyze each option:
NYC-FS01 : Its role "Server" fall under above categories. Hence it can be accessed by using Azure migrate.
BOS-DB01 : Its role "server" fall under above categories. Hence it can be accessed by using Azure migrate.
Sea-CA01 : Its role "CA" does not fall under above categories. Hence it can not be accessed by using Azure migrate.
Hou-NW01 : Its role "DNS" does not fall under above categories. Hence it can not be accessed by using Azure migrate.
Sea-DC01 : Its role "DC" does not fall under above categories. Hence it can not be accessed by using Azure migrate.
Reference:
https://docs.microsoft.com/en-us/azure/migrate/migrate-services-overview
NEW QUESTION # 34
You have an Azure virtual machine that runs Windows Server 2019 and has the following configurations:
Name: VM1
Location: West US
Connected to: VNET1
Private IP address: 10.1.0.4
Public IP addresses: 52.186.85.63
DNS suffix in Windows Server: Adatum.com
You create the Azure DNS zones shown in the following table.
You need to identify which DNS zones you can link to VNET1 and the DNS zones to which VM1 can automatically register.
Which zones should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/dns/private-dns-overview
NEW QUESTION # 35
You need to ensure that User1 can create initiative definitions, and User4 can assign initiatives to RG2. The solution must meet the technical requirements.
Which role should you assign to each user? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.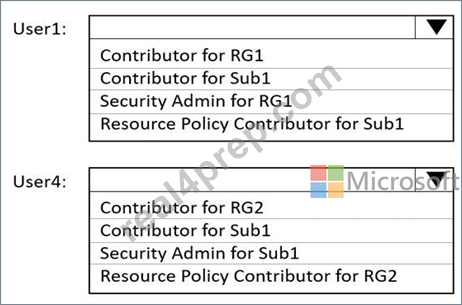
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/governance/policy/overview
NEW QUESTION # 36
You have an availability set named AS1 that contains three virtual machines named VM1, VM2, and VM3.
You attempt to reconfigure VM1 to use a larger size. The operation fails and you receive an allocation failure message.
You need to ensure that the resize operation succeeds.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Stop VM1, VM2 and VM3
2 - Resize VM1
Reference:
https://azure.microsoft.com/es-es/blog/resize-virtual-machines/
NEW QUESTION # 37
You have an Azure subscription that contains the resources shown in the following table.
VM1 connects to VNET1.
You need to connect VM1 to VNET2.
Solution: You create a new network interface, and then you add the network interface to VM1.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Explanation
Instead you should delete VM1. You recreate VM1, and then you add the network interface for VM1.
Note: When you create an Azure virtual machine (VM), you must create a virtual network (VNet) or use an existing VNet. You can change the subnet a VM is connected to after it's created, but you cannot change the VNet.
References:
https://docs.microsoft.com/en-us/azure/virtual-machines/windows/network-overview
NEW QUESTION # 38
You have an Active Directory forest named contoso.com.
You install and configure Azure AD Connect to use password hash synchronization as the single sign-on (SSO) method. Staging mode is enabled.
You review the synchronization results and discover that the Synchronization Service Manager does not display any sync jobs.
You need to ensure that the synchronization completes successfully.
What should you do?
- A. From Azure PowerShell, run Start-AdSyncSyncCycle -PolicyType Initial.
- B. From Synchronization Service Manager, run a full import.
- C. Run Azure AD Connect and set the SSO method to Pass-through Authentication.
- D. Run Azure AD Connect and disable staging mode.
Answer: D
Explanation:
Staging mode must be disabled. If the Azure AD Connect server is in staging mode, password hash synchronization is temporarily disabled.
References:
https://docs.microsoft.com/en-us/azure/active-directory/connect/active-directory-aadconnectsync-troubleshoot-password-hash-synchronization#no-passwords-are-synchronized-troubleshoot-by-using-the-troubleshooting-task
NEW QUESTION # 39
You have an Azure Active Directory (Azure AD) tenant that has Azure AD Privileged Identity Management configured.
You have 10 users who are assigned the Security Administrator role for the tenant.
You need the users to verify whether they still require the Security Administrator role.
What should you do?
- A. From Azure AD Privileged Identity Management, create an access review.
- B. From Azure AD Privileged Identity Management, create a conditional access policy.
- C. From Azure AD Identity Protection, configure a user risk policy.
- D. From Azure AD Identity Protection, configure the Weekly Digest.
Answer: A
NEW QUESTION # 40
You have an Azure subscription named Subscription1. Subscription1 contains the resources in the following table.
In Azure, you create a private DNS zone named adatum.com. You set the registration virtual network to VNet2. The adatum.com zone is configured as shown in the following exhibit.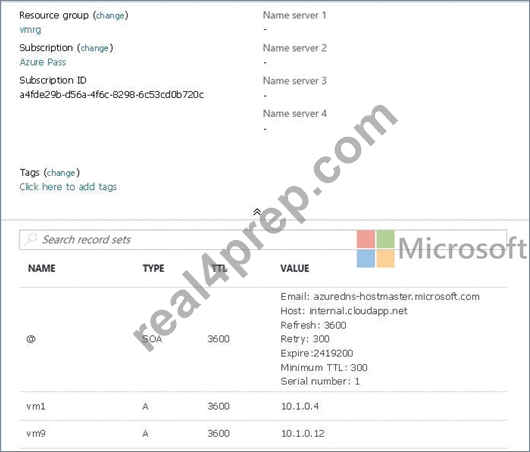
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation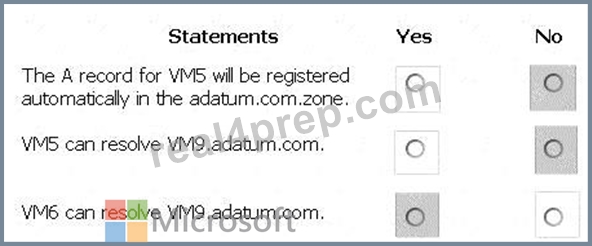
Box 1: No
Azure DNS provides automatic registration of virtual machines from a single virtual network that's linked to a private zone as a registration virtual network. VM5 does not belong to the registration virtual network though.
Box 2: No
Forward DNS resolution is supported across virtual networks that are linked to the private zone as resolution virtual networks. VM5 does belong to a resolution virtual network.
Box 3: Yes
VM6 belongs to registration virtual network, and an A (Host) record exists for VM9 in the DNS zone.
By default, registration virtual networks also act as resolution virtual networks, in the sense that DNS resolution against the zone works from any of the virtual machines within the registration virtual network.
References: https://docs.microsoft.com/en-us/azure/dns/private-dns-overview
NEW QUESTION # 41
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You need to ensure that an Azure Active Directory (Azure AD) user named Admin1 is assigned the required role to enable Traffic Analytics for an Azure subscription.
Solution: You assign the Traffic Manager Contributor role at the subscription level to Admin1
- A. Yes
- B. NO
Answer: B
Explanation:
The Traffic Manager Contributor role is not related to Traffic Analytics. Traffic Manager is a service that provides DNS-based load balancing and traffic routing across different regions and endpoints. Traffic Manager Contributor is a role that allows you to create and manage Traffic Manager profiles, endpoints, and geographies1.
Traffic Analytics is a service that provides visibility into user and application activity in your cloud networks. Traffic Analytics analyzes Azure Network Watcher network security group (NSG) flow logs to provide insights into traffic flow in your Azure cloud. With Traffic Analytics, you can visualize network activity, identify hot spots, secure your network, optimize your network deployment, and pinpoint network misconfigurations2.
To enable Traffic Analytics for an Azure subscription, you need to have a role that grants you the following permissions at the subscription level:
Microsoft.Network/applicationGateways/read
Microsoft.Network/connections/read
Microsoft.Network/loadBalancers/read
Microsoft.Network/localNetworkGateways/read
Microsoft.Network/networkInterfaces/read
Microsoft.Network/networkSecurityGroups/read
Microsoft.Network/publicIPAddresses/read
Microsoft.Network/routeTables/read
Microsoft.Network/virtualNetworkGateways/read
Microsoft.Network/virtualNetworks/read
Microsoft.OperationalInsights/workspaces/*
Some of the built-in roles that have these permissions are Owner, Contributor, or Network Contributor3. However, these roles also grant other permissions that may not be necessary or desirable for enabling Traffic Analytics. Therefore, the best practice is to use the principle of least privilege and create a custom role that only has the required permissions for enabling Traffic Analytics4.
Therefore, to meet the goal of ensuring that an Azure AD user named Admin1 is assigned the required role to enable Traffic Analytics for an Azure subscription, you should create a custom role with the required permissions and assign it to Admin1 at the subscription level.
NEW QUESTION # 42
You have a hybrid deployment of Azure Active Directory (Azure AD) that contains the users shown in the following table.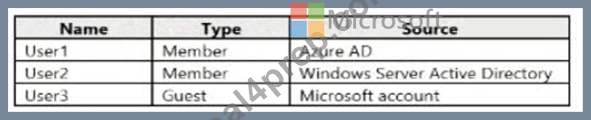
You need to modify the JobTitle and UsageLocation attributes for the users.
For which users can you modify the- attributes from Azure AD? To answer, select the appropriate options in the answer area.

See below answer
Answer:
Explanation:
NEW QUESTION # 43
You have an Azure subscription that contains three virtual networks named VNET1, VNET2, and VNET3.
Peering for VNET1 is configured as shown in the following exhibit.
Peering for VNET2 is configured as shown in the following exhibit.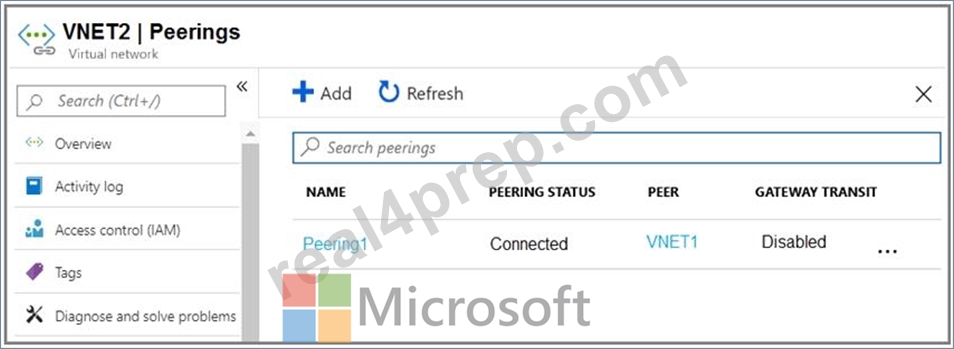
Peering for VNET3 is configured as shown in the following exhibit.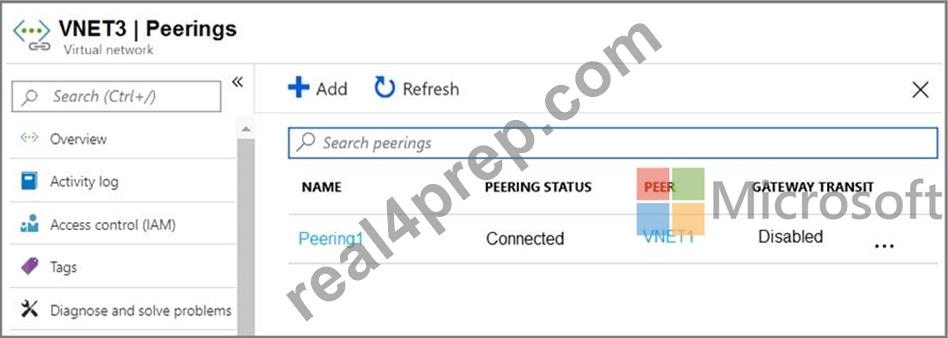
How can packets be routed between the virtual networks? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/virtual-network/virtual-network-peering-overview
NEW QUESTION # 44
You have an Azure web app named WebApp1 that runs in an Azure App Service plan named ASP1. ASP1 is based on the D1 pricing tier.
You need to ensure that WebApp1 can be accessed only from computers on your on-premises network. The solution must minimize costs.
What should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: B1
B1 (Basic) would minimize cost compared P1v2 (premium) and S1 (standard).
Box 2: Cross Origin Resource Sharing (CORS)
Once you set the CORS rules for the service, then a properly authenticated request made against the service from a different domain will be evaluated to determine whether it is allowed according to the rules you have specified.
Note: CORS (Cross Origin Resource Sharing) is an HTTP feature that enables a web application running under one domain to access resources in another domain. In order to reduce the possibility of cross-site scripting attacks, all modern web browsers implement a security restriction known as same-origin policy. This prevents a web page from calling APIs in a different domain. CORS provides a secure way to allow one origin (the origin domain) to call APIs in another origin.
References:
https://azure.microsoft.com/en-us/pricing/details/app-service/windows/
https://docs.microsoft.com/en-us/azure/cdn/cdn-cors
NEW QUESTION # 45
You have an Azure subscription that contains an Azure Storage account.
You plan to create an Azure container instance named container1 that will use a Docker image namedImage1.
Image1 contains a Microsoft SQL Server instance that requires persistent storage.
You need to configure a storage service for Container1.
What should you use?
- A. Azure Table storage
- B. Azure Blob storage
- C. Azure Queue storage
- D. Azure Files
Answer: D
Explanation:
Explanation
https://azure.microsoft.com/en-us/blog/persistent-docker-volumes-with-azure-file-storage/
NEW QUESTION # 46
You have an Azure subscription named Subscription1.
In Subscription1, you create an Azure web app named WebApp1. WebApp1 will access an external service that requires certificate authentication.
You plan to require the use of HTTPS to access WebApp1.
You need to upload certificates to WebApp1.
In which formats should you upload the certificate? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 47
You create a virtual machine scale set named Scale1. Scale1 is configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
Answer:
Explanation:
Explanation:
As cooling period and scale in and scale out durations are not displayed in the graphical view, so we need to consider the default values as below for these settings.
Cool down (minutes) : The amount of time to wait before the rule is applied again so that the autoscale actions have time to take effect. Default is 5 minutes.
Duration : The amount of time monitored before the metric and threshold values are compared. Default is 10 minutes.
Box 1: 4 virtual machines
The Autoscale scale out rule increases the number of VMs by 2 if the CPU threshold is 80% or higher for more than or equals to 10 mins due to default duration for scale in and out is 10 minutes. Since CPU utilization at 85% only lasts for 6 mins , it does not trigger the rules.
Hence no of virtual machines will be same as the initial value which is 4.
Box 2: 4 virtual machines
The Autoscale scale in rule decreases the number of VMs by 4 if the CPU threshold is 30% or lower for more than or equal to 10 mins. due to default duration for scale in and out is 10 minutes . Since CPU utilization at 30% only lasts for 6 mins , it does not trigger the rules. Hence after first 6 mins instance count will be same as initial count as 4. After that CPU utilization reached to 50% for 6 mins , which again would not trigger the scale in rule. Therefore no of virtual machines will be same as the initial value which is 4.
References:
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/autoscale-overview
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/autoscale-best-practices
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/autoscale-common-scale-patterns
NEW QUESTION # 48
You are evaluating the name resolution for the virtual machines after the planned implementation of the Azure networking infrastructure.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Answer:
Explanation: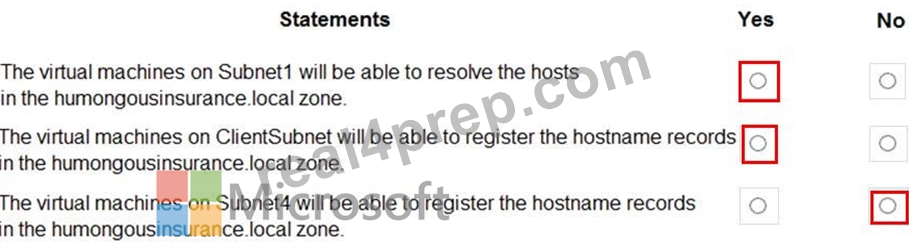
Reference:
https://docs.microsoft.com/en-us/azure/dns/private-dns-overview
https://docs.microsoft.com/en-us/azure/virtual-network/virtual-networks-name-resolution-for-vms-and-role-instances
Topic 2, Litware, inc.
Existing Environment
The network contains an Active Directory forest named Litware.com. All domain controllers are configured as DNS servers and host the Litware.com DNS zone.
Litware has finance, human resources, sales, research, and information technology departments. Each department has an organizational unit (OU) that contains all the accounts of that respective department. All the user accounts have the department attribute set to their respective department. New users are added frequently.
Litware.com contains a user named User1.
All the offices connect by using private links.
Litware has data centers in the Montreal and Seattle offices. Each data center has a firewall that can be configured as a VPN device.
All infrastructure servers are virtualized. The virtualization environment contains the servers in the following table.
Litware uses two web applications named App1 and App2. Each instance on each web application requires 1GB of memory.
The Azure subscription contains the resources in the following table.
The network security team implements several network security groups (NSGs).
Planned Changes
Litware plans to implement the following changes:
* Deploy Azure ExpressRoute to the Montreal office.
* Migrate the virtual machines hosted on Server1 and Server2 to Azure.
* Synchronize on-premises Active Directory to Azure Active Directory (Azure AD).
* Migrate App1 and App2 to two Azure web apps named webApp1 and WebApp2.
Technical Requirements
Litware must meet the following technical requirements:
* Ensure that WebApp1 can adjust the number of instances automatically based on the load and can scale up to five instance*.
* Ensure that VM3 can establish outbound connections over TCP port 8080 to the applications servers in the Montreal office.
* Ensure that routing information is exchanged automatically between Azure and the routers in the Montreal office.
* Enable Azure Multi-Factor Authentication (MFA) for the users in the finance department only.
* Ensure that webapp2.azurewebsites.net can be accessed by using the name app2.Litware.com.
* Connect the New Your office to VNet1 over the Internet by using an encrypted connection.
* Create a workflow to send an email message when the settings of VM4 are modified.
* Create a custom Azure role named Role1 that is based on the Reader role.
* Minimize costs whenever possible.
NEW QUESTION # 49
......
Prepare For Realistic AZ-104 Dumps PDF - 100% Passing Guarantee: https://lead2pass.real4prep.com/AZ-104-exam.html